EKS CNI
CNI, short for Container Network Interface, is a standard for creating plugins that control network communication between containers.
Kubernetes delegates IP assignment and network configuration for pods to the CNI.
AWS developed the VPC CNI, and EKS uses this CNI.
This allows the use of VPC features (such as security groups, VPC flow logs, etc.).
When EKS is installed, VPC CNI pods are automatically created. They are created as a DaemonSet and named aws-node.
If you enter kubectl -n kube-system get ds aws-node to check, you will see:

that it is running like this.
VPC CNI Features #
The core function of VPC CNI is to assign pod IPs and manage communication between pods.
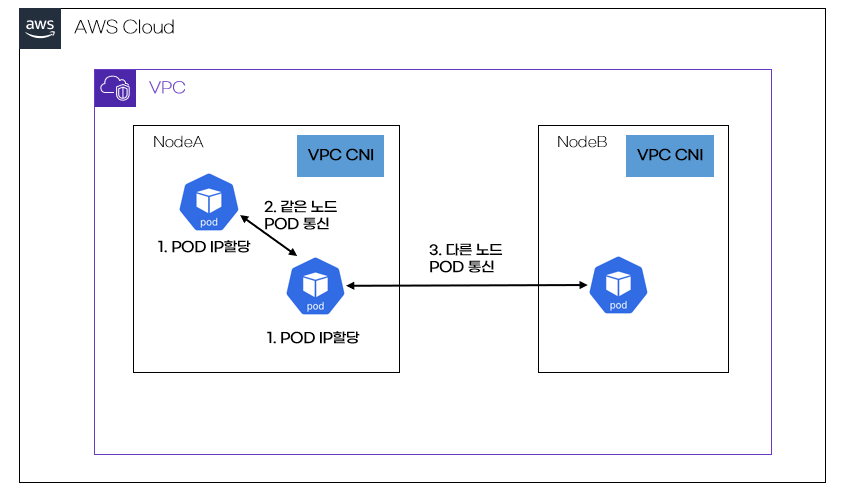
How EKS Assigns IPs to Pods #
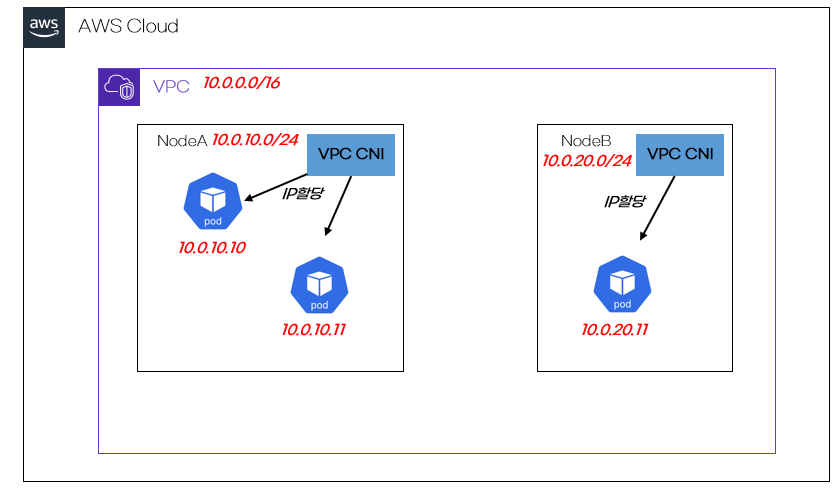
Let's look at how EKS assigns IPs to created pods. When VPC CNI assigns an IP to a pod, it allocates an IP from the node's subnet CIDR range. If nodeA's CIDR is 10.0.10.0/24, then nodeA's pod IPs will belong to the 10.0.10.0/24 range.
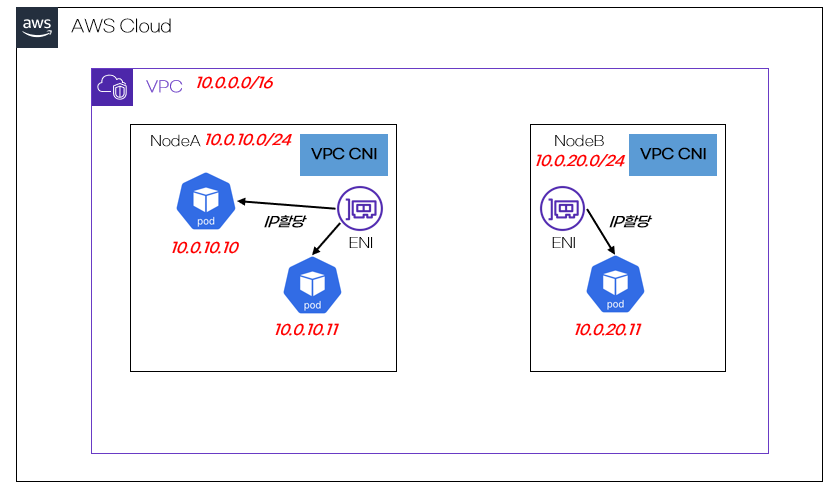
From an AWS perspective, rather than a CNI perspective, the IP assigned by VPC CNI is ultimately an IP assigned to an ENI.
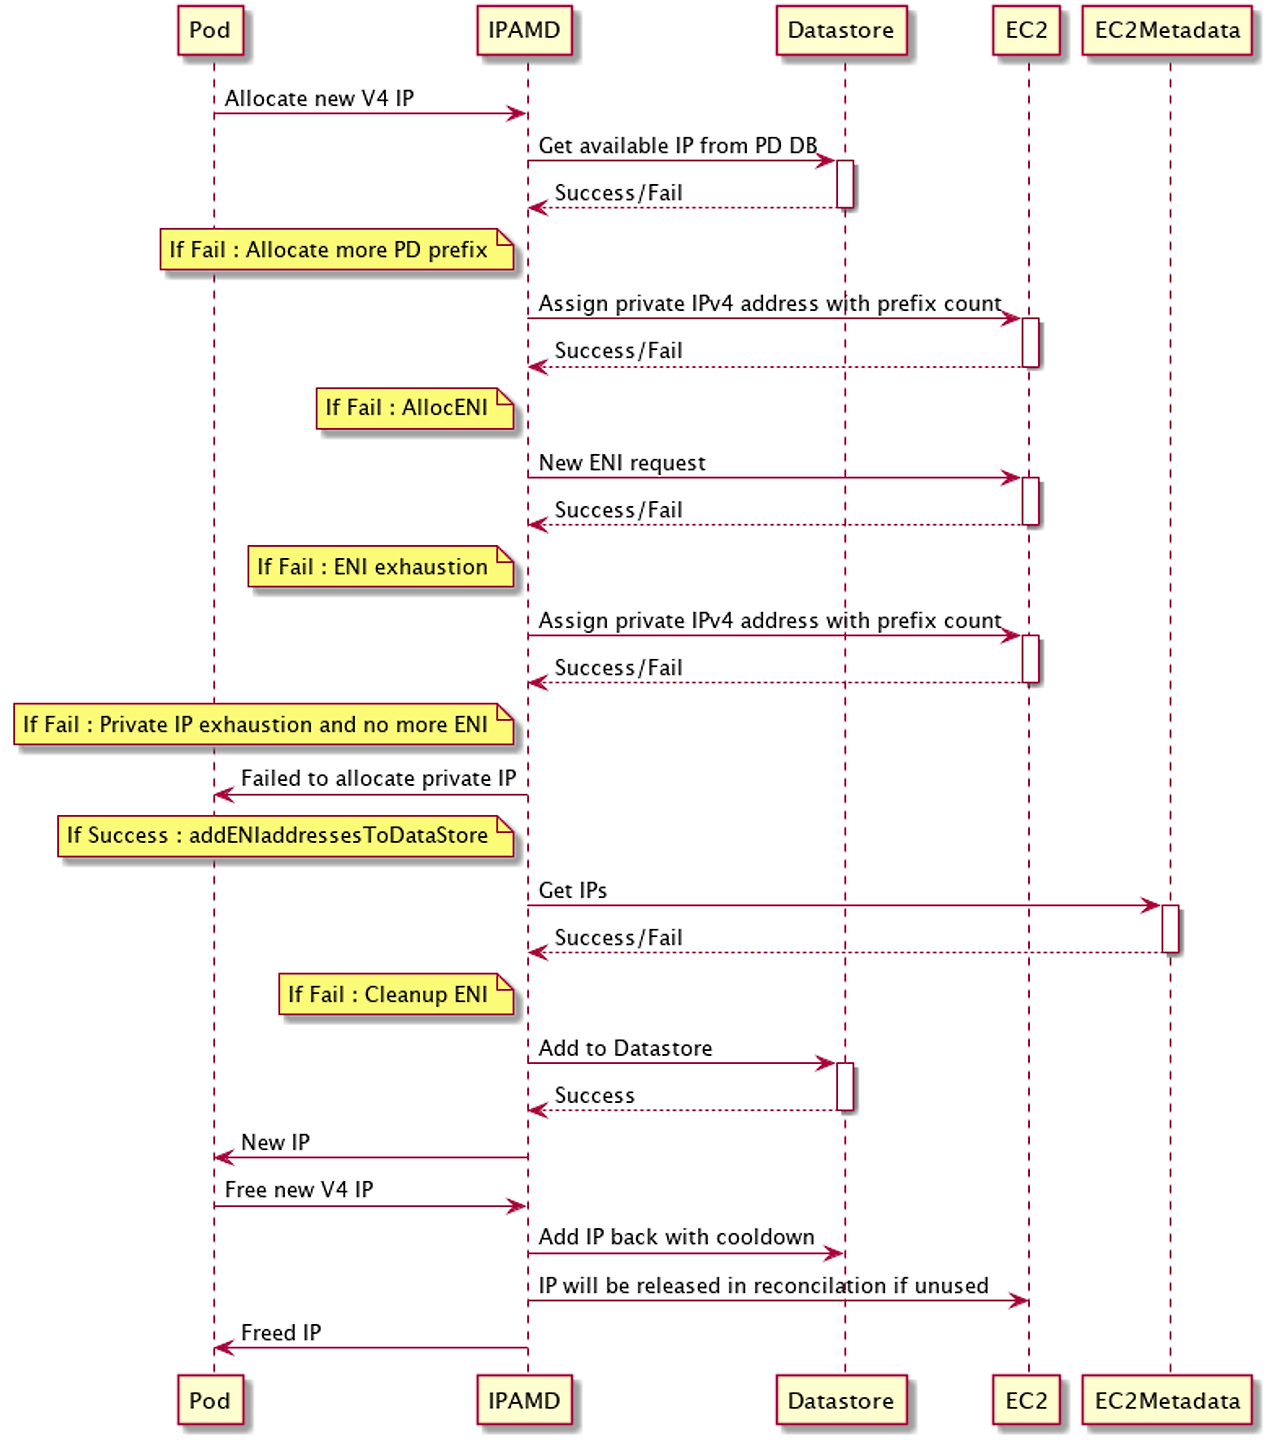
Referring to the AWS blog, the L-PAM daemon within VPC CNI assigns IPs.
[[EKS]]